Match the product to one bounded job
USB Secure may fit a selected encrypted archive workflow after current-version testing. It is not a school media register, recipient-authorization service, guaranteed backup or guaranteed password-recovery mechanism.
Test locker creation, import, lock, reopen, plaintext residue, backup and recovery before any school media data is involved.
Test the complete workflow
- 01Obtain the current installer, documentation, license and supported Windows requirements from official sources.
- 02Create a fictional school media export and a separate fictional access credential.
- 03Test archive creation, import, lock, reopen and file-manifest comparison.
- 04Inspect temporary folders, recent-file lists and source locations for plaintext residue.
- 05Restore a separately stored copy and document password-loss consequences.
Inspect each step in context
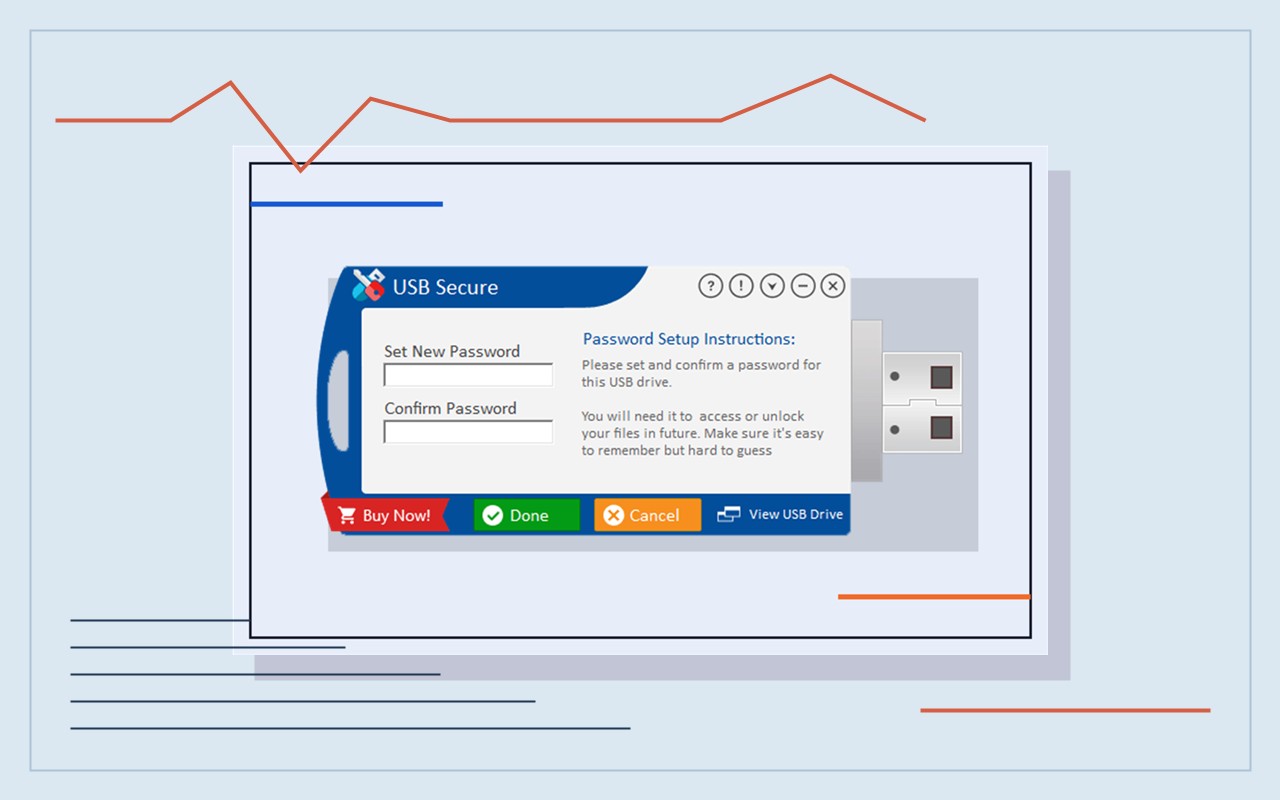
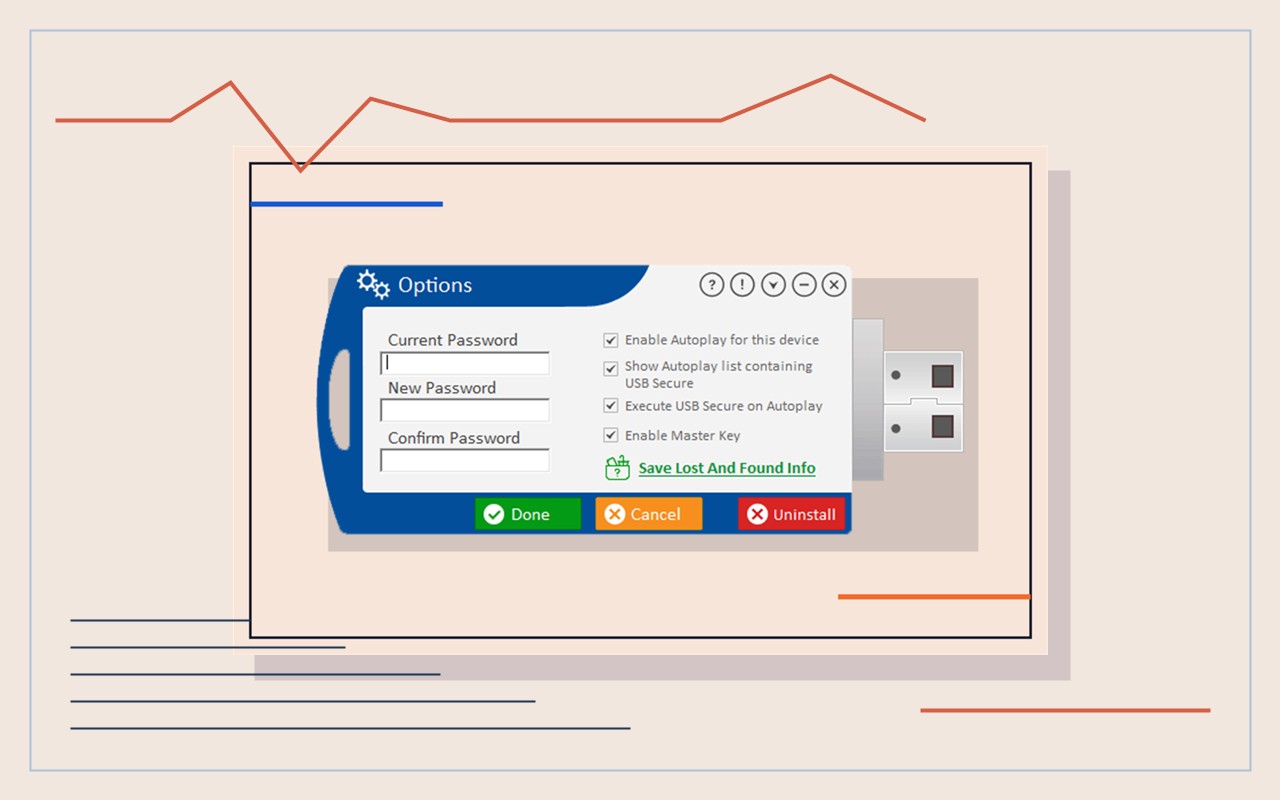
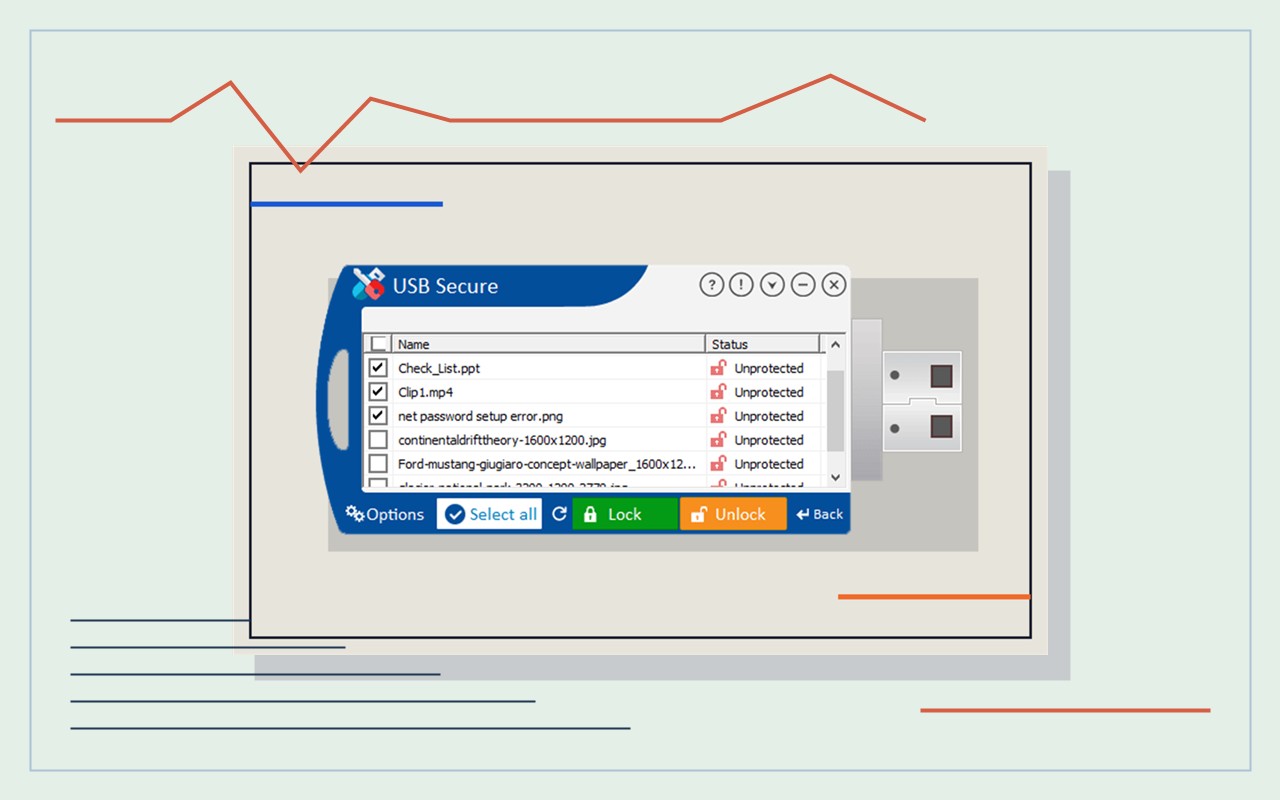
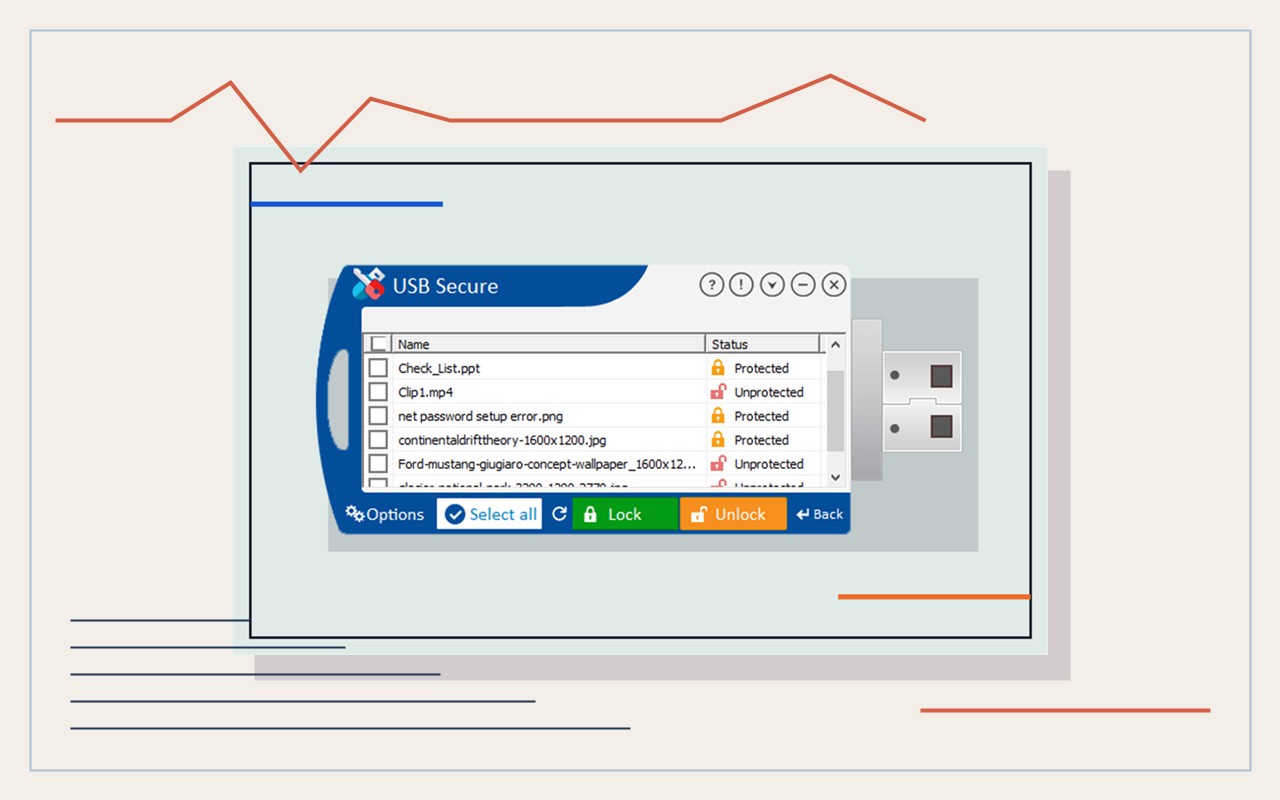
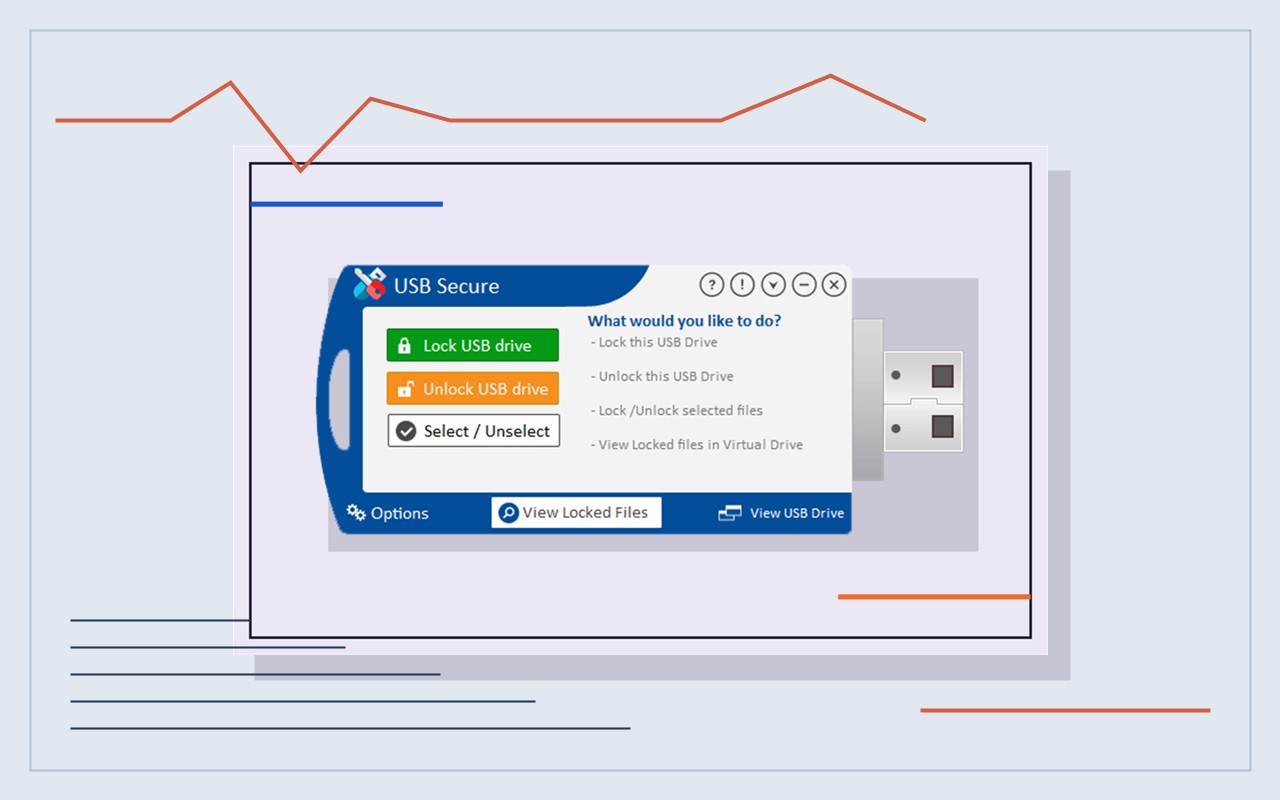
Keep school media controls separate
The product does not establish student media consent, recording accuracy, delivery-access permissions, school delivery roles, recipient authorization, file integrity, platform permissions, guaranteed backup, password recovery or enterprise identity management. It cannot automatically remove plaintext copies created before or after decryption. Treat the school media, the school media workstation account, the recipient acknowledgement and the recovery material as separate record classes. Confirm who is permitted to retain each one, whether the recipient is authorized, and whether platform or engagement rules restrict local copies. A successful locker test does not confirm that a recipient accepted the extract or that the correct manager released it. Keep the authorized recipient acknowledgement outside the encrypted school media archive so it can be consulted during an access problem. Before the school media review begins, document a fallback path that does not require sharing a recipient account password or opening confidential material. After the school media review, review temporary folders, email downloads, browser downloads and sync locations under the authority of the relevant owner. Never promise secure deletion, anonymity or guaranteed recovery on the basis of a product screen alone. Document the current tested release, operating environment and recovery result before adoption. Run the pilot with fabricated school event recordings, then document the school media coordinator approval before introducing real school event recordings. Recheck the workflow after product updates, operating-system changes or storage migrations, because a previously successful test is not permanent evidence of compatibility. Maintain a separate verified recovery copy and a current decision record. Recheck trusted-recipient access whenever circumstances change.
Product questions
Should USB Secure become the school media register?
No. Use it only for a tested, bounded archive role within the approved school media workflow.
Does resetting a password recover an existing archive?
Do not assume so. Test and document the actual recovery path before relying on it.
Primary references
Supplied visuals may depict legacy releases. References support specific boundaries and do not imply endorsement.